








IT security for SMEs in Nuremberg
IT Security Nuremberg: Business Keeps Running
One click on the wrong attachment must not stop your production. Ascend protects SMEs in Nuremberg with five layers and monitors them around the clock.
The principle at a glance
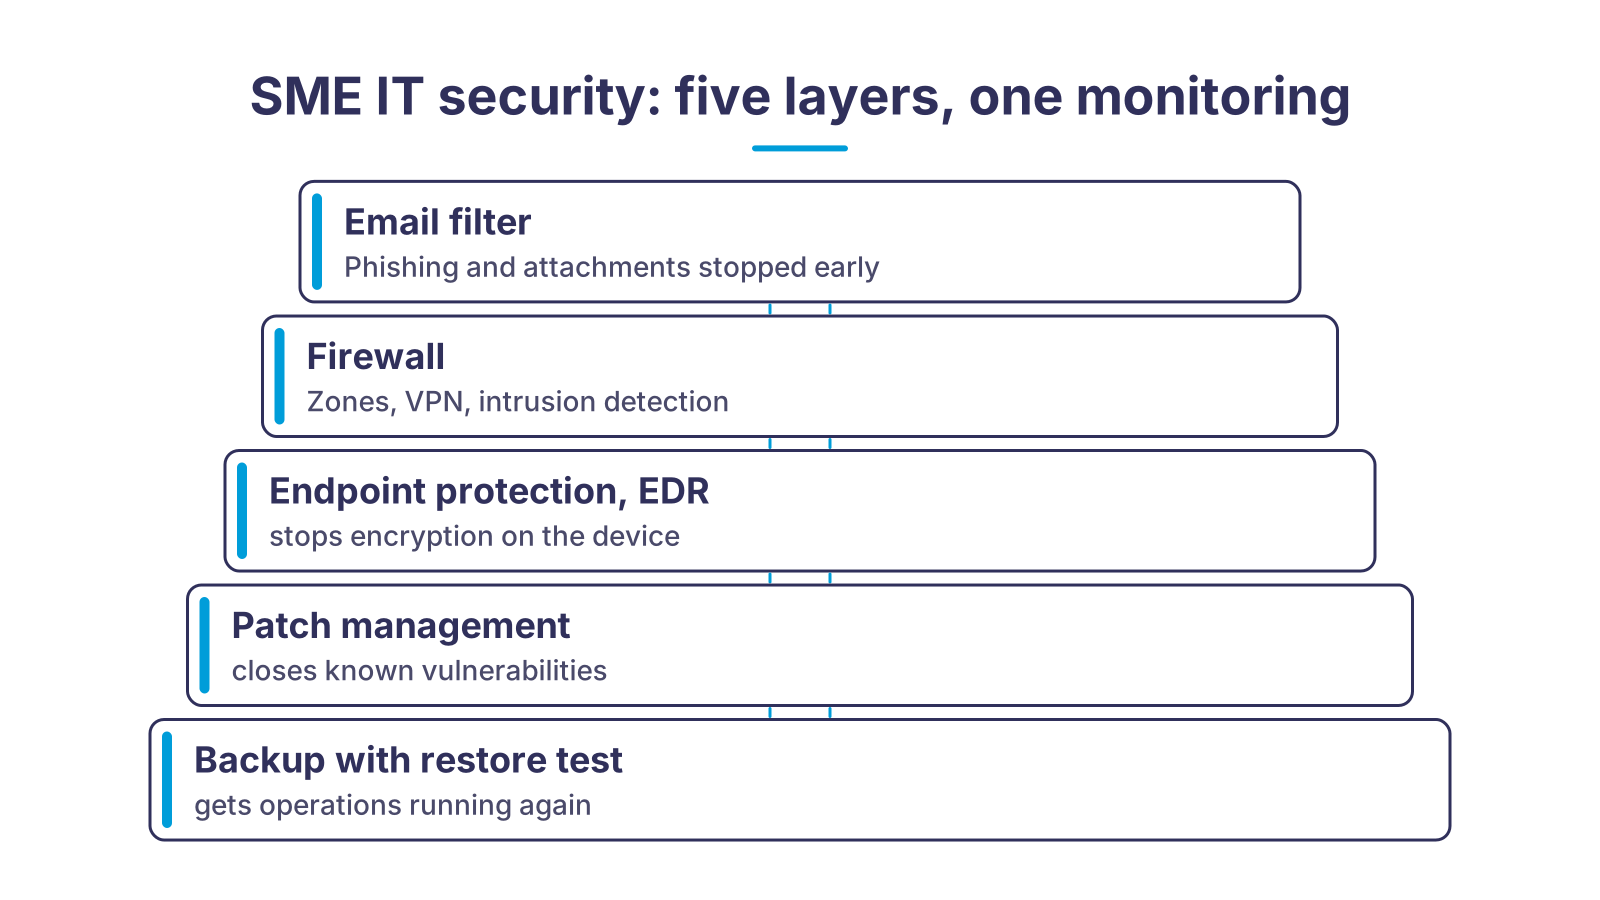
IT security for an SME is not a single product but a stack of five layers. Each one catches what the previous one lets through: the email filter keeps phishing out, the firewall separates the network from the internet, endpoint protection stops malicious code on the computer, patch management closes the gaps it uses to get in, and the backup gets operations running again if something does slip through. Ascend monitors all five layers around the clock.
Five problems we take off your hands
An attack needs several links: an email, an open vulnerability, an unprotected computer, a flat network and data without a backup. For every link in the chain there is a layer that breaks it.
EDR endpoint protection
Patch management
Backup with restore test
Email security
Firewall and segmentation
Emergency plan and 24×7 support
Security check in 4 steps
- 1InventoryWe record servers, workstations, network devices, cloud services and access accounts. Devices that nobody has on their radar any more also end up on the list.
- 2Risk assessmentWe check patch level, backup status, admin rights, email protection and firewall rules, and rank the findings by damage and likelihood.
- 3Action planYou receive a prioritised list with effort and benefit for each measure. What your team can do itself is listed, and so is what we take over.
- 4Implementation and operationWe set up endpoint protection, patch management, backup and email filter, document the emergency plan and look after day-to-day operation. Our support is available around the clock.
What the five layers deliver
| Protects against | What Ascend takes care of | What you notice day to day | |
|---|---|---|---|
| Email security | Phishing, spoofed senders, malicious attachments and links | Set up filter and archiving, maintain rules | Less spam, no invoice trojans in the inbox, mail archived in line with GoB |
| Firewall | Access from outside, spread within the network, unauthorised outbound connections | Set up and manage the firewall, keep rules current, intrusion detection, VPN for home office and field staff | A sealed-off company network, secure connection from on the road |
| EDR endpoint protection | Ransomware, malicious code in documents, misused admin rights | Set up and manage endpoint protection, support available around the clock | An infected computer is isolated instead of infecting the whole network |
| Patch management | Attacks via known vulnerabilities in Windows, browsers, Office and firmware | Distribute updates centrally, document exceptions, bring stragglers up to date | Computers restart on schedule, not in the middle of a presentation |
| Backup with restore test | Data loss from encryption, hardware failure or user error | Develop a backup concept with you, backup checks, restore test | The certainty that your data can really be restored |
Why a virus scanner alone is not enough
Traditional antivirus programs compare files with a list of known malware. Against an attacker who reassembles his tools for your company specifically, that list does not help. Endpoint Detection and Response (EDR) works differently: the agent watches what a process does. If a program starts encrypting hundreds of files in a short time or reading credentials from memory, it is stopped and the computer is taken off the network before the file server is affected.
Ascend relies on SentinelOne for this, which detects threats in real time using machine learning. How the technology works in detail is explained in our article The technology behind SentinelOne; rolling it out in a company is described in Integrating SentinelOne. For an overview of how it differs from classic solutions, see our page Antivirus for businesses.
The second half of the name matters: Response. An alarm at three in the morning is only useful if someone reacts. We run endpoint protection as part of operations, not as an optional extra; our support is available around the clock, and for critical outages SLA contracts set binding response times.
A backup is only a backup after the restore test
The most uncomfortable question after an incident is not “Do you have a backup?” but “When did you last restore it?”. A backup can run empty for months because a drive is full, a password has expired or the backup job fails silently. That is why we develop the backup concept together with you, check the backups and test the restore. An untested backup is not a backup.
What a good concept clarifies: How quickly can individual files or whole servers be recovered? Is there a copy outside the company network that an encryption attack in the office cannot reach, for example in encrypted cloud storage? And how long are older versions kept in case damage is only noticed late?
The restore test also shows how long a recovery really takes. That experience belongs in the emergency plan, so that in a real incident everyone knows what comes back first.
Email as an entry point
A typical attack on a small or medium-sized business begins with an email: a supposed invoice, a job application with an attachment, a message from the “managing director” asking for an urgent transfer. The best protection is that this message never reaches the mailbox. Ascend relies on Hornetsecurity services for this: spam and phishing filters, checking of attachments and links, protection against spoofed senders.
Archiving is part of it too. Incoming and outgoing mail is stored unalterably, employees can flag private mail that is protected from access by auditors, and the archive complies with the German principles of proper accounting (GoB) that apply to companies in Germany. If a mailbox is ever encrypted or deleted, the correspondence is still available. Details are on our page Email security with Hornetsecurity.
Technology alone is not enough here, though. Anyone in the company who approves payments needs a second confirmation through another channel, and every admin account belongs behind a second factor. Hardware keys based on the FIDO2 standard are the most robust option, because they cannot be captured by phishing.
What Ascend takes on as an IT systems house in Nuremberg
Ascend has been an IT systems house in Nuremberg since 2010 and supports small and medium-sized businesses from Nuremberg and Franconia as a managed service provider. For IT security that means: we do not just supply the licence, we set it up, look after it and react when something stands out. Our monitoring catches many faults before anyone in the business notices; support is available 24×7.
A firewall is more than the rule “inside may go out, outside may not come in”. A business firewall works at the same time as a router, VPN router, DHCP and DNS server, and uses intrusion detection and prevention to spot attack patterns in live traffic. We choose the right firewall for each site: for small to mid-sized offices it can be a compact gateway such as the Ubiquiti UniFi Cloud Gateway Max; the choice depends on throughput, number of zones and the need for VPN tunnels. You will find further models in the shop collection Firewalls and security.
Much of this can be combined with your existing infrastructure. If you already use our monitoring, you get security support from the same source. We connect home office, field staff and additional sites by VPN; as a managed service we look after the firewall and VPN components including the firewall rules, and our page Site networking shows the options. You will find all services around network, servers and support on our page IT systems house Nuremberg. After setup we stay in operation: patches, backup checks, restore tests and the care of endpoint protection and firewall run with us, not on the side at your end.
The one rule we give every SME
No admin account without a second factor, no user with permanent admin rights. A stolen password with too many privileges is a common route to the server. A FIDO2 hardware key for every administrator and separate accounts for everyday work and administration cost little and take away the attacker's direct path to the server.
Matching licences and hardware in the Ascend shop
In managed operation we use SentinelOne and Hornetsecurity. The products below are the route for companies that want to run the protection themselves: a gateway, licences from other vendors for endpoint and email protection, cloud storage for the backup and a hardware key, all available in the Ascend shop. Which solution suits you, we clarify in the security check.
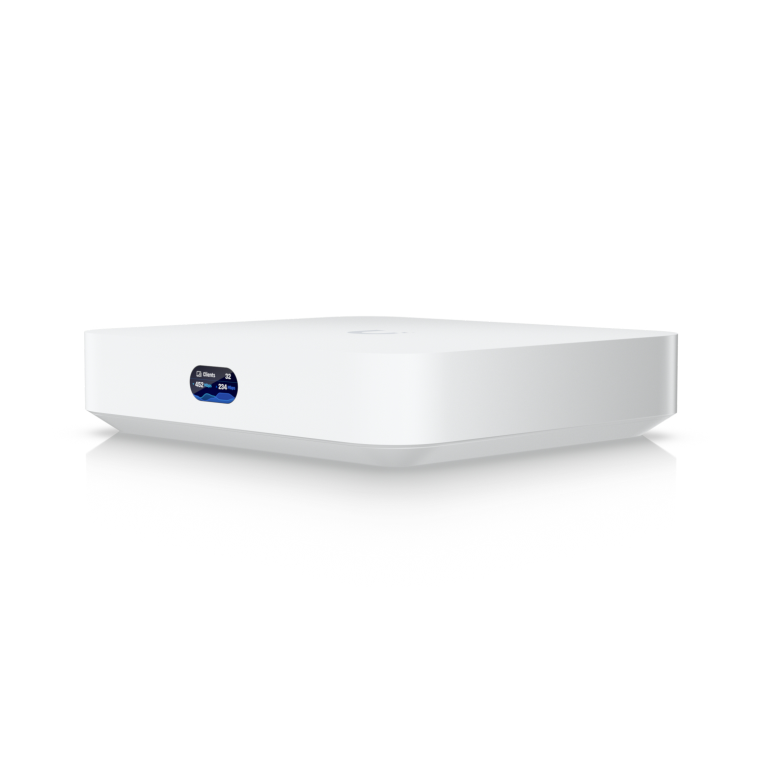
Ubiquiti UniFi Cloud Gateway Max
Compact gateway with firewall, VLAN segmentation and central management for small to mid-sized offices.
- ThreatDown Advanced (1–24 licences, 12 months)
ThreatDown Advanced (1–24 licences, 12 months)
Core protection with endpoint detection and response, patch management, firewall management and managed threat hunting for small teams.
- Sophos Email (25–49 users, 24 months)
Sophos Email (25–49 users, 24 months)
Email filter against spam, phishing and malicious attachments before the message reaches the mailbox.
- Acronis Cloud Storage 500 GB (1 year)
Acronis Cloud Storage 500 GB (1 year)
Encrypted cloud storage for the offsite backup, which survives even if the server in the office has been encrypted.
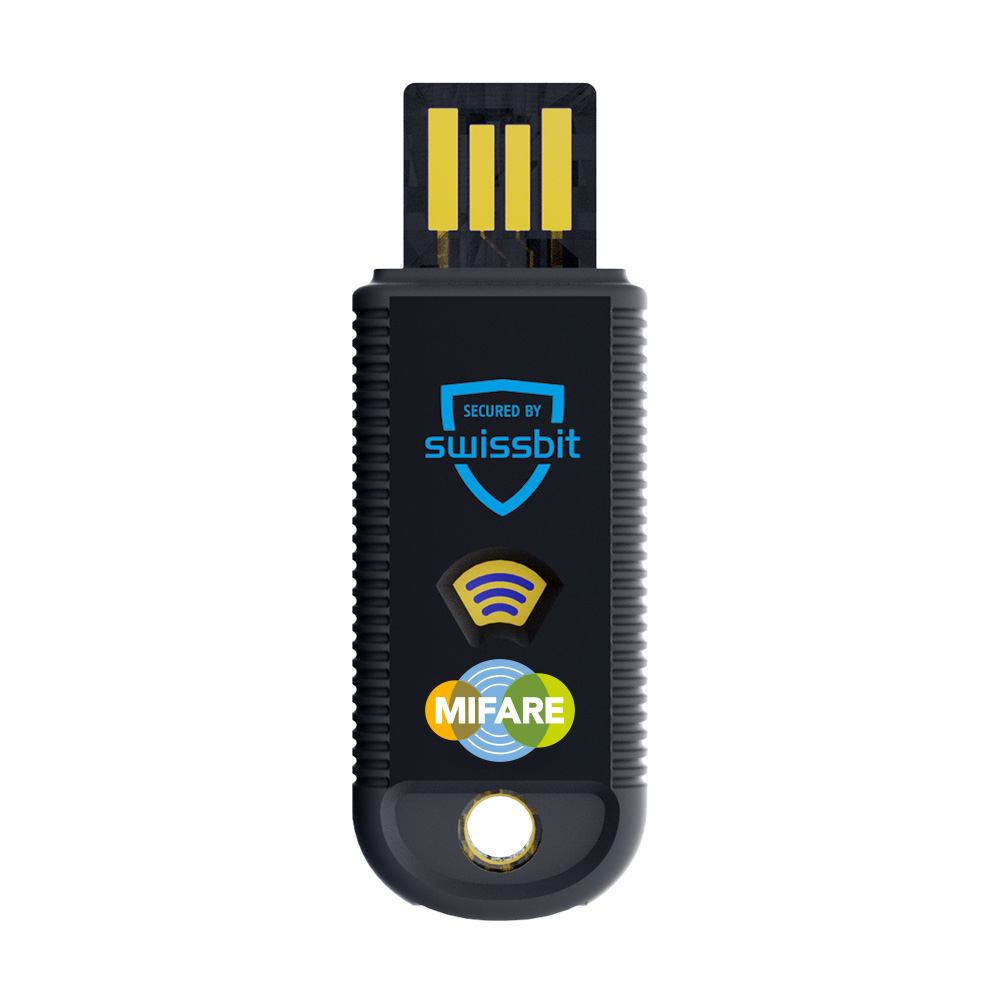
Swissbit iShield Key 1.1 FIDO2
Hardware key for two-factor sign-in to Microsoft 365, Google and other FIDO2 services.
Frequently asked questions about IT security in Nuremberg
Further links
Security check for your company in Nuremberg
Tell us how many workstations and servers you run and what worries you. We will get back to you with an appointment for the inventory.
We look forward to hearing from you!
Tell us the number of workstations, servers and sites, and your question about IT security. We will get back to you shortly with a proposed date for the security check.