Keine Log4j Sicherheitslücken bei ASCEND

Nuremberg, January 2022 – In December 2021, a vulnerability rated as extremely critical was discovered in the widely used Java library Log4j. It allows cybercriminals to easily gain access to a target server in order to execute malware or take control of the system. ASCEND reacted immediately and examined all systems for this vulnerability. "Our hardware manufacturers and software partners closed the rarely exploited gaps very quickly," explains Johannes Fickeis, Managing Director of ASCEND GmbH.
No Log4j vulnerability at Peplink
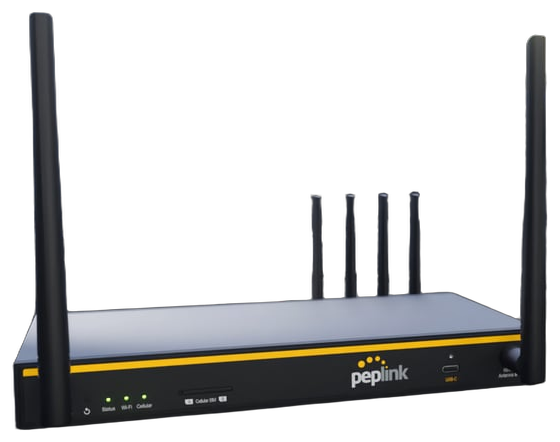
Peplink routers, including the InControl and InControl 2 applications, are not affected by the security vulnerability because they do not use the Log4j framework.
More information about Peplink here.
Matching Products
Matching hardware straight from the ASCEND shop — availability and prices are shown on the product detail page.
Request a consultation
Do you have questions about this solution or want to take your network to a professional level? Our certified technicians will be happy to advise you — from initial analysis all the way to production rollout.
Frequently Asked Questions
Related Links
This article was researched and written with AI assistance and reviewed prior to publication by Ascend's certified technicians.
Ready for your next project?
Talk to our team about your requirements.